InfoSec Stories
A long-term body of practical cybersecurity knowledge, research, analysis, projects and lessons drawn from real security operations work.
Writing & research · SIEM · Windows internals · Linux
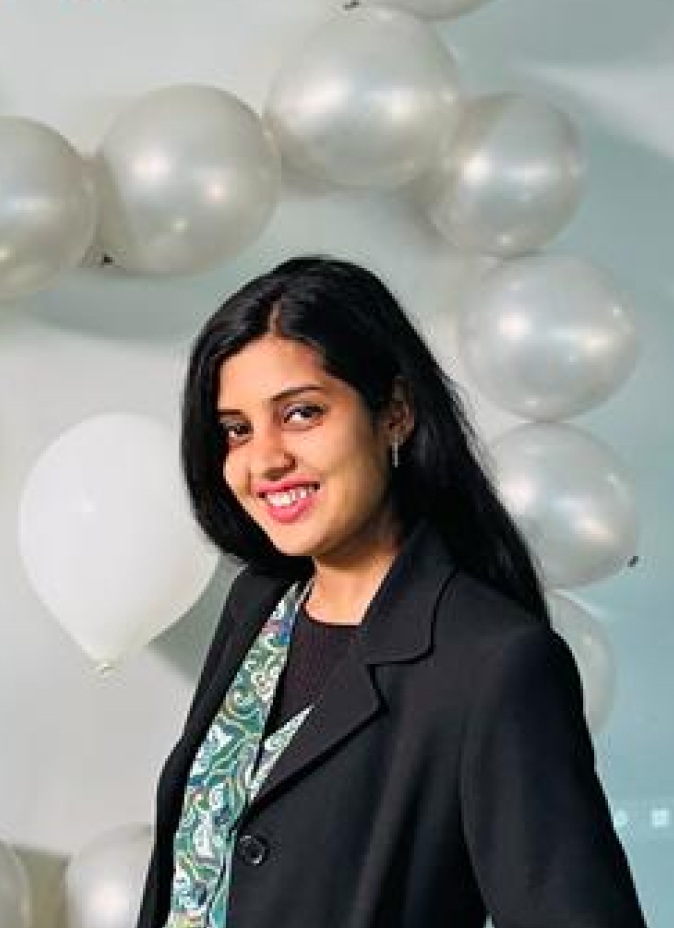
Head of Security Operations
Cybersecurity Practitioner • Security Researcher
Building stronger security operations, detection capabilities, and practical cybersecurity knowledge.
SIEM · SOC · Incident Response · Threat Hunting
DFIR · Threat Intelligence · Security Automation
Introduction
I'm Shreenkhala Bhattarai, Head of Security Operations at CryptoGen Nepal. I've spent the last several years inside a 24/7 SOC: first as an analyst on shift, then leading the team, and now running the operation. I work across SIEM, incident response and threat hunting, with a particular interest in turning security data into useful detections.
Alongside operations I research things like detection bypass, logging strategy and SOC effectiveness, and publish InfoSec Stories. I also teach cybersecurity and mentor incident response practitioners.
Tools I work withLogRhythm · Logpoint · FortiSIEM · Splunk · Wazuh · Fortinet · TheHive · Cortex · Zeek · Suricata
Projects & Research
A long-term body of practical cybersecurity knowledge, research, analysis, projects and lessons drawn from real security operations work.
Writing & research · SIEM · Windows internals · Linux
Hypothesis-driven hunts across client environments, including research into detection bypass techniques in Active Directory and how to close those gaps.
MITRE ATT&CK · Windows Event Logs · Sysmon · Zeek · Suricata
A structured lifecycle for SIEM detection content, from threat research and use case design through testing, tuning and measurable ATT&CK coverage.
SIEM correlation rules · MITRE ATT&CK · Sigma-style logic · AttackIQ
Initiative
Research, detection guidance, project write-ups and lessons learned from years inside security operations.
Explore InfoSec StoriesField Notes
Observe, Orient, Decide, Act: how a fighter-pilot decision framework maps onto SOC monitoring, triage and incident response, and why tempo wins.
The most repeated line in security is only half true. Where the asymmetry cliché breaks down, and how defense-in-depth flips it back on the attacker.
How attackers evade common Active Directory detections, and the audit policy, telemetry and mitigation changes that take those blind spots away.